
Cybersecurity Awareness Training
We make cybersecurity training engaging, practical, and relevant to the everyday risks your team encounters.
Keep Your Team Aware of the Latest Cyber Threats
Your employees are both your first line of defense and a potential point of risk. Human error remains a leading cause of data breaches, ransomware infections, and successful phishing attempts. Carden IT Services’ cybersecurity awareness training equips your workforce with the knowledge and skills needed to recognize and stop cyber threats before they cause harm.

Why Cybersecurity Awareness Training Is Essential
Cyber threats continue to change, and remote and hybrid working models have increased exposure to phishing, social engineering, and credential misuse. In many cases, security incidents are caused not by intent, but by a lack of understanding. Educating your staff helps reduce risk across the entire organization and strengthens your overall security defenses.
Benefits of Cybersecurity Awareness Training
- Lowers the risk of human error and improves your security posture
- Supports compliance with data protection regulations such as GDPR
- Encourages a shared responsibility for cybersecurity across your workforce
- Helps uncover vulnerabilities before they can be exploited by attackers
- Works seamlessly alongside Carden IT Services’ managed cyber defense solutions
What Our Cybersecurity Awareness Training Covers
Our training programs are designed to make every employee a confident and proactive part of your cybersecurity strategy. We combine education with interactive simulations and testing to support long-term behavioral change.
Password Manager Education
Multi Factor Authentication Guidance
Phishing Awareness
Social Engineering Prevention
What Is Social Engineering?
Social engineering is a type of cyber-attack that targets people rather than technical systems. Instead of exploiting software vulnerabilities, attackers rely on manipulation, impersonation, and psychological tactics to trick individuals into sharing sensitive information, clicking malicious links, or granting access to secure systems. These attacks are often carefully crafted to look legitimate, which makes them difficult to detect without proper awareness.
An attacker may pretend to be a coworker, vendor, or senior leader and use urgency, authority, or familiarity to pressure someone into acting quickly. Common examples include claims that an account has been locked, requests for login credentials, or fake IT support calls asking for remote access. Once trust is established, attackers can move deeper into systems, steal data, or enable additional attacks. Recognizing these techniques is a critical step in preventing security incidents.
Social Engineering Training
Carden IT Services’ Social Engineering Training equips your team with the skills needed to recognize manipulation tactics and respond appropriately. We break down how attackers create urgency, impersonate trusted contacts, or apply emotional pressure to push employees into bypassing normal safeguards.
Using practical demonstrations and real-world scenarios, employees learn how to validate requests, question unusual behavior, and handle sensitive information safely.
The training also addresses common attack methods such as pretexting, baiting, impersonation, and fraudulent phone calls. By understanding how these techniques are used, staff are better prepared to spot threats before damage occurs.
The objective is to build confidence across your workforce, reinforce your human layer of security, and ensure every employee plays an active role in defending against cyber threats.

Who Faces the Greatest Risk?
Larger and geographically distributed organizations are often more exposed, as employees may not personally know everyone they interact with. Remote and hybrid working models can increase this risk further, since email and phone requests now replace many face to face interactions.
-
Senior Leadership
Executives are frequently targeted due to their access to sensitive information and authority over financial decisions. -
Finance and Accounting Teams
Often targeted with invoice fraud, payment redirection, and impersonation schemes. -
IT Administrators
Compromised administrator accounts can give attackers broad control across systems and data. -
New or Temporary Staff
Employees who are less familiar with internal processes may be more likely to trust unexpected or unusual requests.
How Carden IT Services Supports Social Engineering Defense
- Security Awareness Training: We educate your team on how to recognize manipulation techniques, confirm identities, and confidently decline suspicious or unusual requests.
- Ethical Testing and Simulation: Our cybersecurity specialists perform controlled testing, including simulated social engineering scenarios, to assess how employees respond in real world situations.
- Clear Reporting and Recommendations: Each exercise is followed by a detailed report that highlights vulnerabilities, explains potential risks, and outlines practical steps for improvement.
By increasing awareness and building confidence, your workforce becomes a proactive layer of defense rather than a potential point of failure.
Phishing Simulation Training
Teach Your Team to Identify and Block Phishing Attacks
Phishing simulation training gives your organization a safe way to evaluate how employees respond to realistic phishing attempts without exposing systems to real risk.
Carden IT Services designs controlled and customized phishing simulations that replicate common attacker techniques, such as urgent requests, look alike domains, and authentic looking branding. Employee interactions are tracked to understand who opens messages, clicks links, or attempts to submit credentials.
The purpose of these simulations is education, not punishment. After each exercise, participants receive clear feedback explaining what indicators were missed and how to recognize similar threats in the future.
Over time, regular simulations improve awareness, reduce risky behavior, and strengthen your organization’s ability to defend against real world phishing attacks.
What Are Phishing Emails?
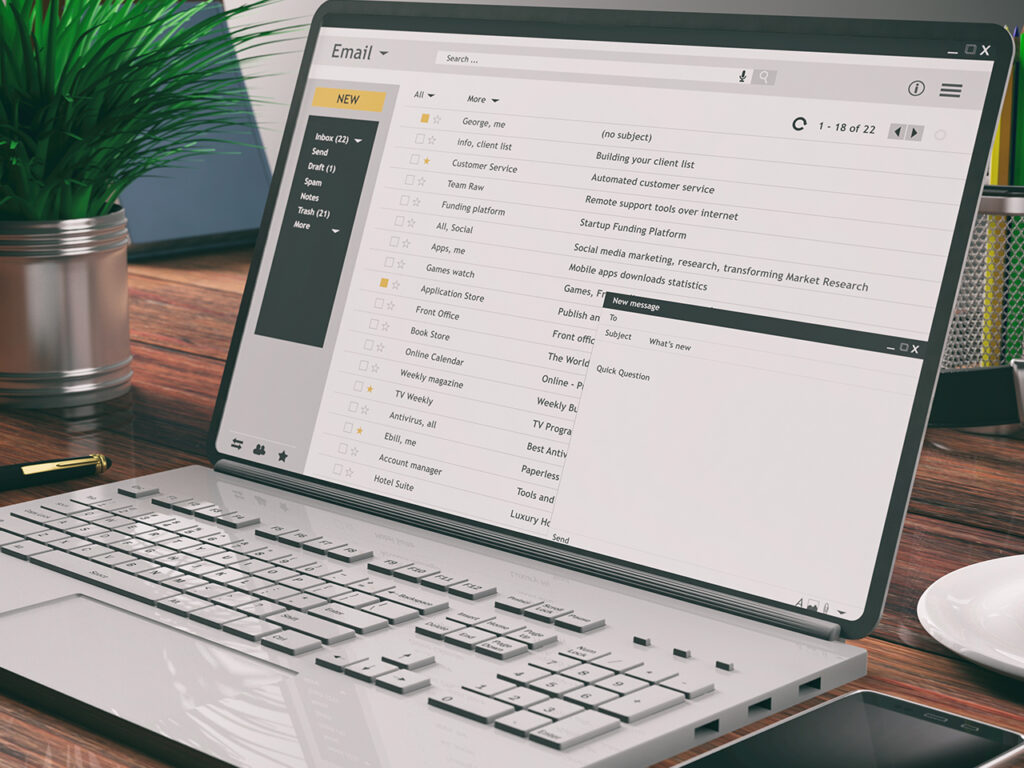
Phishing emails are deceptive messages created to look like they come from a legitimate source. Their goal is to trick recipients into taking unsafe actions or sharing sensitive information. These emails often:
- Impersonate trusted companies, vendors, or coworkers
- Create a sense of urgency with messages such as “action required” or “verify now”
- Include unsafe links or malicious attachments
- Use misleading domain names that closely resemble real ones, such as nnicrosoft.com instead of microsoft.com
More targeted attacks, commonly referred to as spear phishing, are aimed at specific individuals such as executives, administrators, or finance staff in order to gain higher value access.
What Are the Risks of Phishing?
Phishing is one of the most serious cyber risks because a single mistake can give attackers a foothold inside your environment. When an employee clicks on a malicious link or submits credentials on a fake website, criminals can use that access to move deeper into systems, steal information, or compromise business accounts.
Common risks associated with phishing attacks include:
- Ransomware infections that encrypt critical data
- Theft of usernames, passwords, or financial information
- Data breaches that damage customer confidence and brand reputation
- Regulatory violations that may lead to fines or penalties under GDPR
- Compromised accounts that can be reused for further attacks

How Our Phishing Simulation Program Works
Carden IT Services delivers safe and realistic phishing simulations to your team at varied intervals. These messages are designed to closely resemble real world threats, such as internal announcements or supplier communications, without putting your systems at risk.
When a user clicks a link or attempts to submit information, they are immediately shown a short and supportive training message that explains the warning signs that were missed.
- If a user correctly reports or avoids the simulated phishing email, they receive positive reinforcement to strengthen good security habits.
- By running these simulations on an ongoing basis, awareness stays high and employees remain prepared to recognize and respond to real phishing attempts as they occur.
This ongoing process ensures that awareness remains high and that your staff are always prepared for real-world phishing attacks.

Benefits of Phishing Simulation Training
- Builds stronger awareness and encourages faster recognition of phishing attempts
- Helps reinforce secure habits through interactive, practical training
- Reveals which teams or individuals may need additional education or support
- Provides clear metrics that show your organization’s current phishing risk level

Partner with Carden IT Services
Effective cybersecurity goes beyond technology. It depends on informed and confident people. Carden IT Services delivers complete cybersecurity awareness programs that equip your team with the knowledge to recognize threats, strengthen defenses, and lower the risk of data breaches.
Our US-based specialists provide customized training sessions, realistic phishing simulations, and detailed reporting as part of our managed cyber defense services. This approach helps ensure your workforce plays an active role in protecting your organization.